Tag: risk management

  • Australian Retailers Link TradingView to Brokers to Track Currency Swings

    Australian Retailers Link TradingView to Brokers to Track Currency Swings

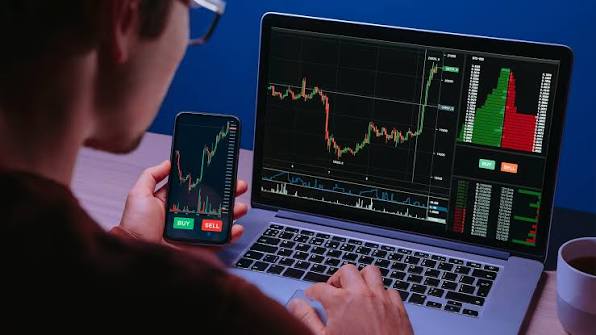
    Australian retail importers are turning to TradingView to monitor foreign exchange movements and freight-linked oil prices before supply chain shifts impact quarterly margins.

    The software pairs live market feeds with execution accounts at regulated brokers such as EasyMarkets, which has operated since 2001, allowing operators to respond to price swings without switching screens.

    How Live Feeds Connect to Trading Desks

    TradingView operates as an analytical interface rather than a custodian of funds. The platform pulls historical and live pricing data across foreign exchange pairs, freight-sensitive commodities, and equity indices into customizable chart layouts.

    To place market orders, users link the platform directly to third-party brokerage accounts. Regulated brokers such as EasyMarkets, established in 2001 and licensed by the Australian Securities and Investments Commission alongside the Cyprus Securities and Exchange Commission, handle execution through fixed-spread models without charging trade commissions.

    Managing Exposure on Inbound Shipments

    Most retail operators sourcing stock from Asian manufacturing hubs face exposure to the Australian dollar against the US dollar and regional currencies. Freight charges also fluctuate with global crude oil benchmarks.

    Tracking these inputs in real time allows procurement managers to identify price pressures weeks before supplier invoices arrive. Automated tools, including guaranteed stop-loss orders and negative balance protection, give businesses predefined price exits if market movements accelerate against their open positions.

    Risks in Derivative Contracts

    Direct hedging through contracts for difference carries distinct balance-sheet hazards for non-financial companies. CFDs track underlying price movements without conferring ownership of physical commodities or currency reserves, amplifying both gains and losses through borrowed capital.

    ASIC maintains public guidance warning commercial operators about derivative risk controls. Retail businesses using charting software must separate speculative positions from baseline inventory budgeting to avoid unexpected cash outflows during currency sell-offs.

    Balancing Tools Against Central Bank Benchmarks

    The move toward integrated technical charting follows prolonged margin compression across Australian import sectors. Operators that previously relied solely on end-of-month bank statements now monitor daily exchange rate channels to negotiate supplier pricing terms.

    Businesses tracking Australian dollar trends without opening trading accounts can cross-reference platform indicators with official foreign exchange rate datasets published daily by the Reserve Bank of Australia.

  • Ping an Bank Approves AI Rules After Deploying over 450 Use Cases

    Ping an Bank Approves AI Rules After Deploying over 450 Use Cases

    Ping An Bank has approved internal management rules for artificial intelligence, becoming the first listed Chinese lender to formally adopt an AI governance framework.

    The Shenzhen-listed lender announced the board-approved measures in a filing on Wednesday, following a push by regulators for banks to strengthen oversight of AI use.

    Board oversight and risk tiers

    By the end of June, the bank had rolled out more than 450 large-model AI use cases across marketing, investment advice, compliance and risk control, according to its interim report.

    Operational AI risks are classified into distinct tiers and folded into the bank’s enterprise risk-management system. While the lender confirmed the board approval in a regulatory filing, it has not published the full text of the rules.

    Scale of deployment across lenders

    All 42 A-share listed commercial banks in mainland China referenced AI deployments in their interim financial reports this year. Several other listed lenders are preparing matching compliance rules to meet state regulatory requirements.

    Across the region, formalising AI governance shifts the technology from experimental pilots to audited core infrastructure. The operational risk lies in compliance execution. Internal oversight mechanisms must keep pace with rapid deployment without choking automated workflow efficiency.

    Hong Kong sandbox and cross-border testing

    Regulators in neighbouring Hong Kong are pushing financial firms to adopt autonomous systems while maintaining cross-border compliance standards. In March, financial authorities expanded a supervised generative AI sandbox to include securities brokerages, insurance underwriters and pension funds. The program first launched for retail banks in 2024.

    Financial Secretary Paul Chan Mo-po stated that Hong Kong provides a testing environment for model training, data security and cross-border financial data flows under common law standards. Gary Ng, senior economist for Asia-Pacific at Natixis, noted that the city operates as “a perfect place to test and apply the standards of different jurisdictions in an increasingly fragmented world”.

    Regulatory requirements and earlier steps

    The governance measures implement binding guidelines issued in June by the National Financial Regulatory Administration. Those rules require mainland commercial banks and licensed insurers to assume direct institutional liability for autonomous systems. They also mandate board-level supervision of algorithm deployment.

    International financial groups are running similar integration programs across Asia and Europe. HSBC launched its HSBCnio corporate data platform in late September to connect institutional accounts directly to client AI tools. Barclays expanded its automated software engineering tools across retail and wholesale units.

    Attention now turns to the remaining A-share lenders as third-quarter disclosures approach. Those filings will show which state-owned and joint-stock commercial banks follow Ping An Bank in publishing board-approved AI governance structures.

  • Why Singapore’s Retailers Need to Take Heed of Recent Supply Chain Cyber Incidents

    Why Singapore’s Retailers Need to Take Heed of Recent Supply Chain Cyber Incidents

    As cyber threats continue to rise, understanding the impact of these threats and how they infiltrate the retail supply chain is vital for operational continuity. Singapore’s recently refreshed Industry Digital Plan (IDP) for the retail sector highlighted enhanced cyber hygiene measures for protection at different stages of growth.

    The region’s booming digital economy makes businesses operating here a prime target for cyberattacks. The retail sector is ripe for third-party cyberattacks, with threat actors exploiting vulnerabilities in Point-of-Sale (POS) terminals, supply chain systems, logistics platforms, and other interconnected technologies.

    Recent Cyber Attacks Targeting Supply Chains

    The retail industry has been shaken by a number of high-profile reported cyber incidents recently, affecting major players like Marks and Spencer (M&S) and Harrods.

    Closer to home, popular bubble tea chain Chica San Chen disclosed a data breach of one of its vendors’ servers, compromising the personal information of members, such as their names, mobile numbers, e-mail addresses and login passwords. In 2024, Filipino fast-food giant Jolibeewas reportedly subjected to a major data breach affecting the data of 11 million customers.

    These incidents not only tarnish brand reputations, but also disrupt operations and expose sensitive customer data, causing widespread concern. The financial fallout from these compromises highlights the crucial need for retailers to focus more diligently on the security of their digital and physical supply chains.

    According to BlueVoyant research, more than 70% of Singaporean organisations reported an average of 3.97 breaches impacting operations. Almost half (47%) of Singapore organisations indicated the news of breaches over the past 12 months are likely to lead to an increase in budget for additional internal and external resources to help protect against supply chain cyber security issues.

    Retail Under Growing Threat

    Threat actors like DragonForce have reportedly boldly claimed responsibility for a series of attacks targeting UK retailers, often partnering with groups like Scattered Spider to amplify their reach. Understanding the motivations and methods of these groups provides invaluable insight — such as exploiting supply chain vulnerabilities — to predict and prevent future attacks. Their evolving strategies represent a constant threat that requires ongoing vigilance and continuous improvements to third-party risk management practices in retailers.

    Retail businesses are often vulnerable to a catalogue of common cyber threats, including phishing schemes, ransomware, and supply chain compromises. Threat actors leverage malware and sophisticated social engineering to infiltrate retailers’ defences. By embedding malicious software within trusted channels, they can access secure areas usually safeguarded but overlooked in anticipation of direct attacks.

    In fact, more than a third (35%) of Singapore respondents to BlueVoyant research said they have no way of autonomously seeing the cyber risk posture of third parties and rely on self-reporting. This knowledge underscores the necessity for robust cyber security practices targeting every link in the retail supply chain.

    Harden defences and manage supply chain risk

    Singapore’s Cyber Security Agency (CSA)’s toolkit for enterprises highlight key areas for organisations to address increasing cyber risks, including the need for a third-party risk management programme to assess and manage the risks posed by third parties, including vendors, products, and services.

    Implementing effective third-party risk management practices, characterised by strong cross-business collaboration in vendor management, continuous cyber threat monitoring across the supply chain, and robust due diligence procedures, is essential for ensuring comprehensive visibility of risks associated with key suppliers.

    Additionally, both retailers and their suppliers must prioritise robust employee training in cyber security best practices, empowering them to recognise and respond to suspicious activity. Implementing multi-factor authentication adds an extra layer of security, making it significantly more difficult for unauthorised users to compromise the integrity systems. Securing helpdesk authentication can also help prevent deceptive access attempts, ensuring that customer service channels remain protected.

    Proactive incident response planning is crucial for effectively managing breaches, should they occur, with an eye towards the potential for a cross-business compromise. Retailers work with many suppliers and partners and so must maintain even greater vigilance within their extended ecosystem. Establishing network segmentation, sharing only strictly necessary data, and implementing access controls can help make sure that a potentially compromised vendor does not cause a cascade of issues.

    Regular drills and collaboration with cyber security partners can help ensure incident management is more seamless, minimising potential damage through quick containment and eradication. By embracing these defensive strategies, retailers can significantly bolster their security posture.

    As cyber threats become increasingly sophisticated, it is imperative for retailers in the region to maintain constant vigilance and adaptability in their cyber security posture. Ensuring robust protection of these essential services is vital due to their immediate impact on society’s well-being. Retailers must heed the call to integrate recommended cyber security measures, protecting themselves against potential compromises.

    By William Oh, Head of Asia Pacific, BlueVoyant