Tag: third party

  • Third-Party App Store Aptoide Games Launches on Google Play: Heres What You Need to Know

    Third-Party App Store Aptoide Games Launches on Google Play: Heres What You Need to Know

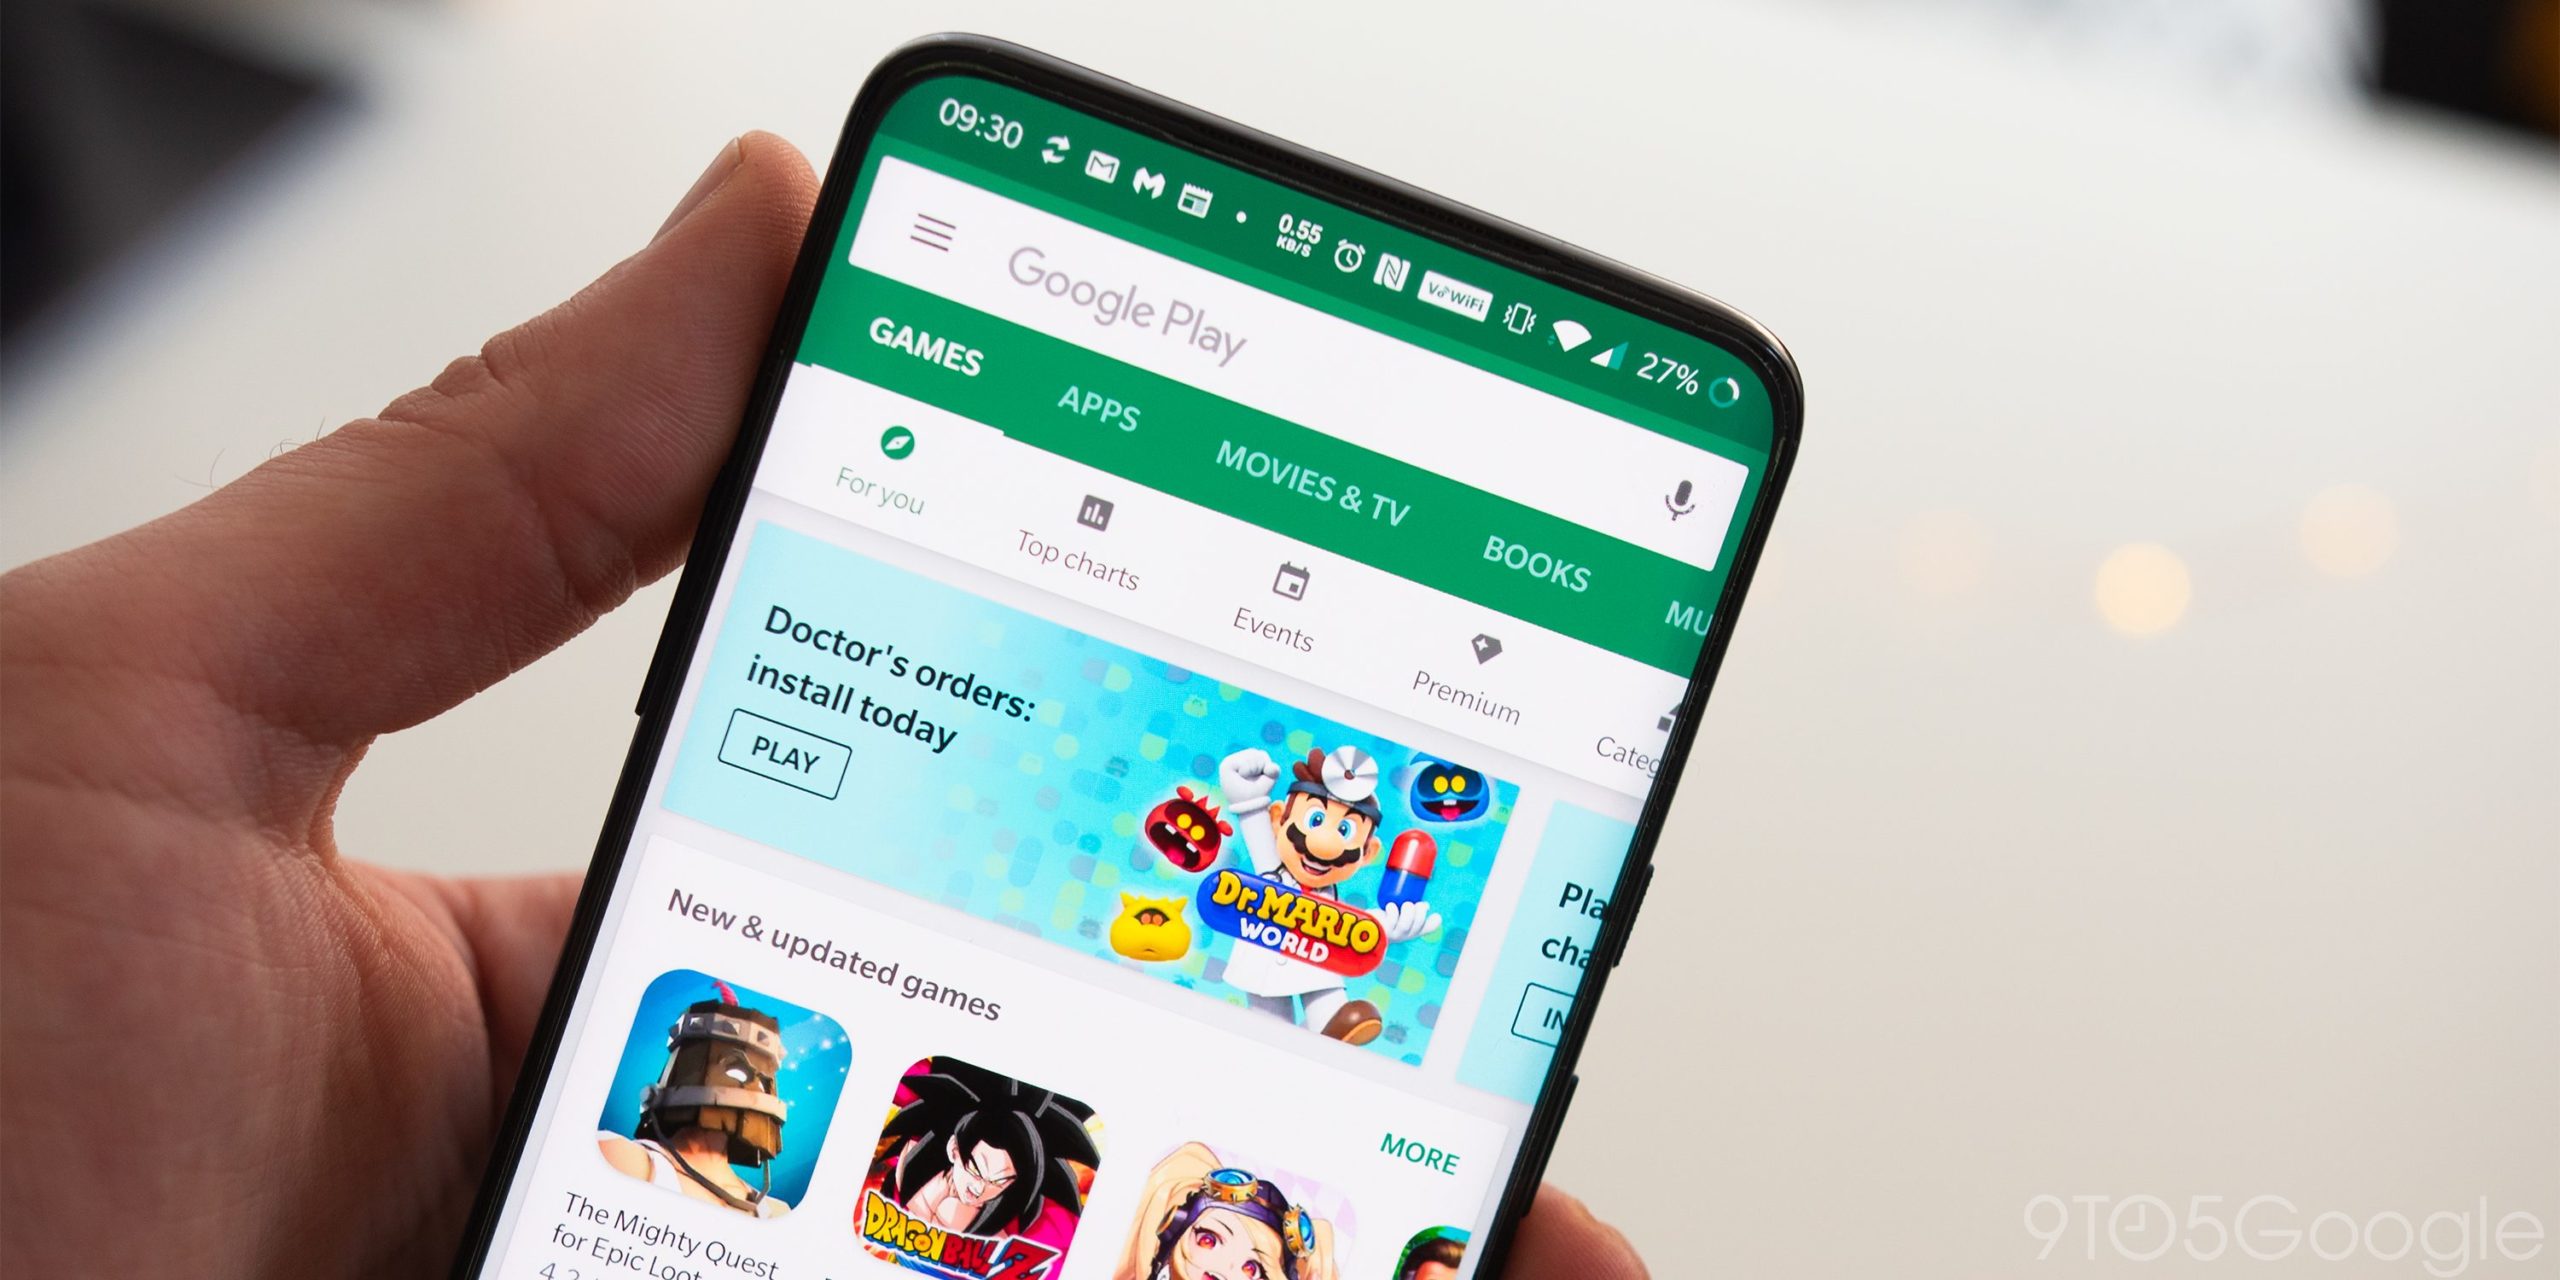
    The Google Play Store is now offering a new third-party app outlet known as Aptoide Games, featuring a variety of free and paid games. Accessing this new store is straightforward; simply launch the Play Store app on your Android device, tap on the profile icon located in the upper right corner, and scroll down the menu until you find the “Third-party app stores” option.

    Exploring Aptoide Games: A Third-Party App Store within Google Play

    Upon clicking, you are presented with a list of third-party app stores available, currently headlined by Aptoide Games. By selecting this entry, you are directed to an installation button for the alternative app store.

    The Aptoide Games platform offers an array of applications available for installation, including:

    – Huawei Health: An app that tracks your health metrics, workouts, and calorie consumption on any Android 6.0 or higher device, regardless of whether it’s a Huawei product or not.
    – Clash of Kings: A real-time strategy game that thrusts you into the shoes of a lord responsible for constructing a castle.
    – Vikings: War of Clans PvP: A game that makes you a Viking chieftain tasked with building a stronghold, training armies, and participating in both player vs player and player vs environment battles.
    – Legend of Mushroom: This role-playing game allows you to embark on a journey to become human as a mushroom character.
    – LUDUS: Merge Arena PvP: A game where you can collect and upgrade over 100 unique heroes for arena combat.
    – Wartune Ultra: A mobile strategy-based role-playing game where you command a city and ally with others to combat the forces of darkness.
    – Saint Seiya: Legend of Justice: This game tasks you with assembling the ultimate underworld team to dominate the Sanctuary War as Hades arrives.
    – Duck Survival: A roguelike shooter game with thrilling survival scenarios against zombies and giant bosses.
    – The Ants: Underground Kingdom: An immersive game where an ant colony endeavors to survive crises, protect the Queen, and construct an anthill.

    The Backstory: Why Google Now Allows Third-Party App Stores

    The presence of third-party app stores within Google Play Store stems from court orders resulting from the Epic Games v Google lawsuit. The conflict began when Epic Games, developer of Fortnite, sued Google over the 30% commission it took on in-app purchases. To circumvent this fee, Epic Games implemented a direct payment system within Fortnite, which violated Play Store’s regulations.

    Following the introduction of this direct payment system, Google removed Fortnite from the Play Store on August 13, 2020. This event sparked lawsuits that ultimately compelled Google to permit third-party apps within the Play Store. Notably, while Google lost a significant antitrust lawsuit initiated by Epic Games, Apple triumphed in most of its 2021 legal skirmish with Epic and is not subject to the same court order as Google.

    Questions & Answers

    What is Aptoide Games?
    Aptoide Games is a third-party app store accessible via Google Play Store. It offers a variety of free and paid games.

    How can I access Aptoide Games?
    To access Aptoide Games, open your Google Play Store app, tap on the profile icon, scroll down the menu until you find the “Third-party app stores” option, and click to view.

    Why does Google now allow third-party app stores within Play Store?
    Google’s decision to allow third-party app stores is due to a court order that came about as a result of the Epic Games v Google lawsuit.
  • Why Singapore’s Retailers Need to Take Heed of Recent Supply Chain Cyber Incidents

    Why Singapore’s Retailers Need to Take Heed of Recent Supply Chain Cyber Incidents

    As cyber threats continue to rise, understanding the impact of these threats and how they infiltrate the retail supply chain is vital for operational continuity. Singapore’s recently refreshed Industry Digital Plan (IDP) for the retail sector highlighted enhanced cyber hygiene measures for protection at different stages of growth.

    The region’s booming digital economy makes businesses operating here a prime target for cyberattacks. The retail sector is ripe for third-party cyberattacks, with threat actors exploiting vulnerabilities in Point-of-Sale (POS) terminals, supply chain systems, logistics platforms, and other interconnected technologies.

    Recent Cyber Attacks Targeting Supply Chains

    The retail industry has been shaken by a number of high-profile reported cyber incidents recently, affecting major players like Marks and Spencer (M&S) and Harrods.

    Closer to home, popular bubble tea chain Chica San Chen disclosed a data breach of one of its vendors’ servers, compromising the personal information of members, such as their names, mobile numbers, e-mail addresses and login passwords. In 2024, Filipino fast-food giant Jolibeewas reportedly subjected to a major data breach affecting the data of 11 million customers.

    These incidents not only tarnish brand reputations, but also disrupt operations and expose sensitive customer data, causing widespread concern. The financial fallout from these compromises highlights the crucial need for retailers to focus more diligently on the security of their digital and physical supply chains.

    According to BlueVoyant research, more than 70% of Singaporean organisations reported an average of 3.97 breaches impacting operations. Almost half (47%) of Singapore organisations indicated the news of breaches over the past 12 months are likely to lead to an increase in budget for additional internal and external resources to help protect against supply chain cyber security issues.

    Retail Under Growing Threat

    Threat actors like DragonForce have reportedly boldly claimed responsibility for a series of attacks targeting UK retailers, often partnering with groups like Scattered Spider to amplify their reach. Understanding the motivations and methods of these groups provides invaluable insight — such as exploiting supply chain vulnerabilities — to predict and prevent future attacks. Their evolving strategies represent a constant threat that requires ongoing vigilance and continuous improvements to third-party risk management practices in retailers.

    Retail businesses are often vulnerable to a catalogue of common cyber threats, including phishing schemes, ransomware, and supply chain compromises. Threat actors leverage malware and sophisticated social engineering to infiltrate retailers’ defences. By embedding malicious software within trusted channels, they can access secure areas usually safeguarded but overlooked in anticipation of direct attacks.

    In fact, more than a third (35%) of Singapore respondents to BlueVoyant research said they have no way of autonomously seeing the cyber risk posture of third parties and rely on self-reporting. This knowledge underscores the necessity for robust cyber security practices targeting every link in the retail supply chain.

    Harden defences and manage supply chain risk

    Singapore’s Cyber Security Agency (CSA)’s toolkit for enterprises highlight key areas for organisations to address increasing cyber risks, including the need for a third-party risk management programme to assess and manage the risks posed by third parties, including vendors, products, and services.

    Implementing effective third-party risk management practices, characterised by strong cross-business collaboration in vendor management, continuous cyber threat monitoring across the supply chain, and robust due diligence procedures, is essential for ensuring comprehensive visibility of risks associated with key suppliers.

    Additionally, both retailers and their suppliers must prioritise robust employee training in cyber security best practices, empowering them to recognise and respond to suspicious activity. Implementing multi-factor authentication adds an extra layer of security, making it significantly more difficult for unauthorised users to compromise the integrity systems. Securing helpdesk authentication can also help prevent deceptive access attempts, ensuring that customer service channels remain protected.

    Proactive incident response planning is crucial for effectively managing breaches, should they occur, with an eye towards the potential for a cross-business compromise. Retailers work with many suppliers and partners and so must maintain even greater vigilance within their extended ecosystem. Establishing network segmentation, sharing only strictly necessary data, and implementing access controls can help make sure that a potentially compromised vendor does not cause a cascade of issues.

    Regular drills and collaboration with cyber security partners can help ensure incident management is more seamless, minimising potential damage through quick containment and eradication. By embracing these defensive strategies, retailers can significantly bolster their security posture.

    As cyber threats become increasingly sophisticated, it is imperative for retailers in the region to maintain constant vigilance and adaptability in their cyber security posture. Ensuring robust protection of these essential services is vital due to their immediate impact on society’s well-being. Retailers must heed the call to integrate recommended cyber security measures, protecting themselves against potential compromises.

    By William Oh, Head of Asia Pacific, BlueVoyant